Researchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli Data
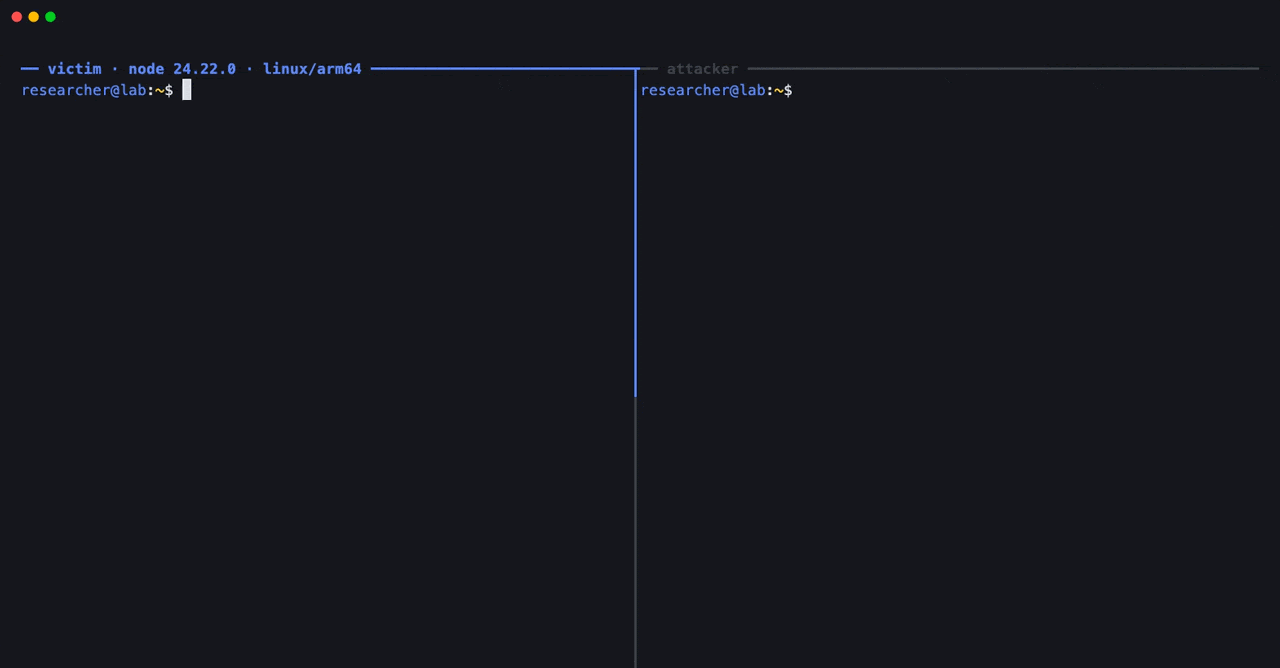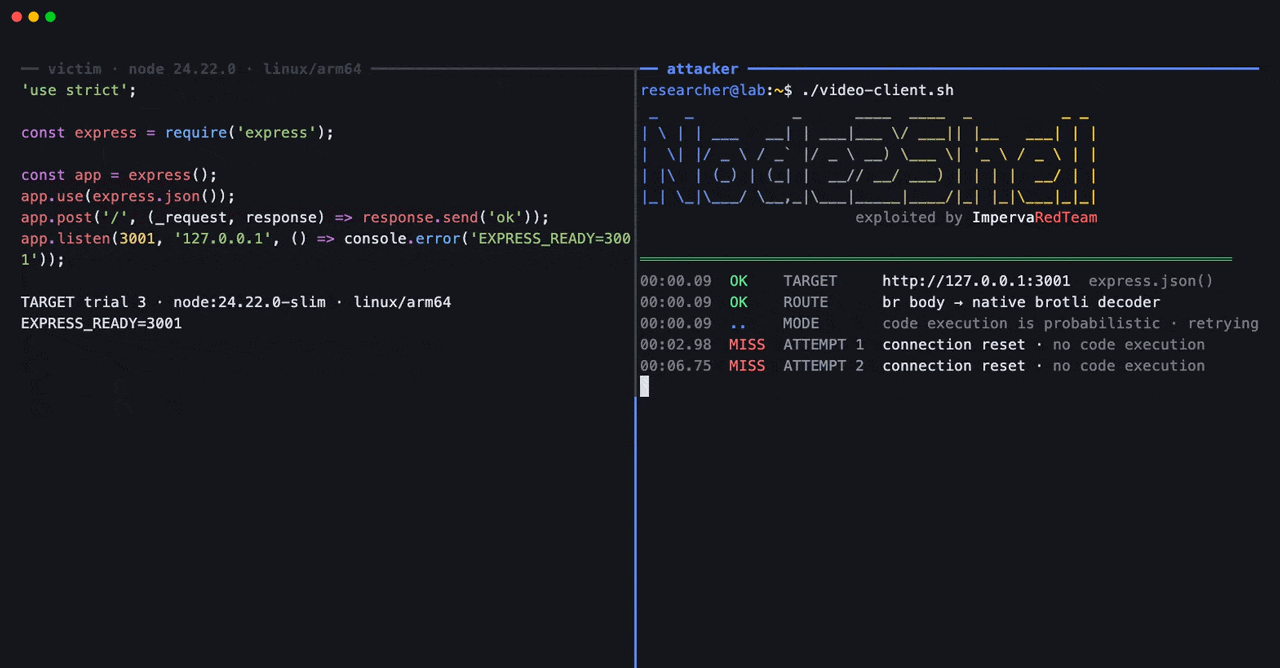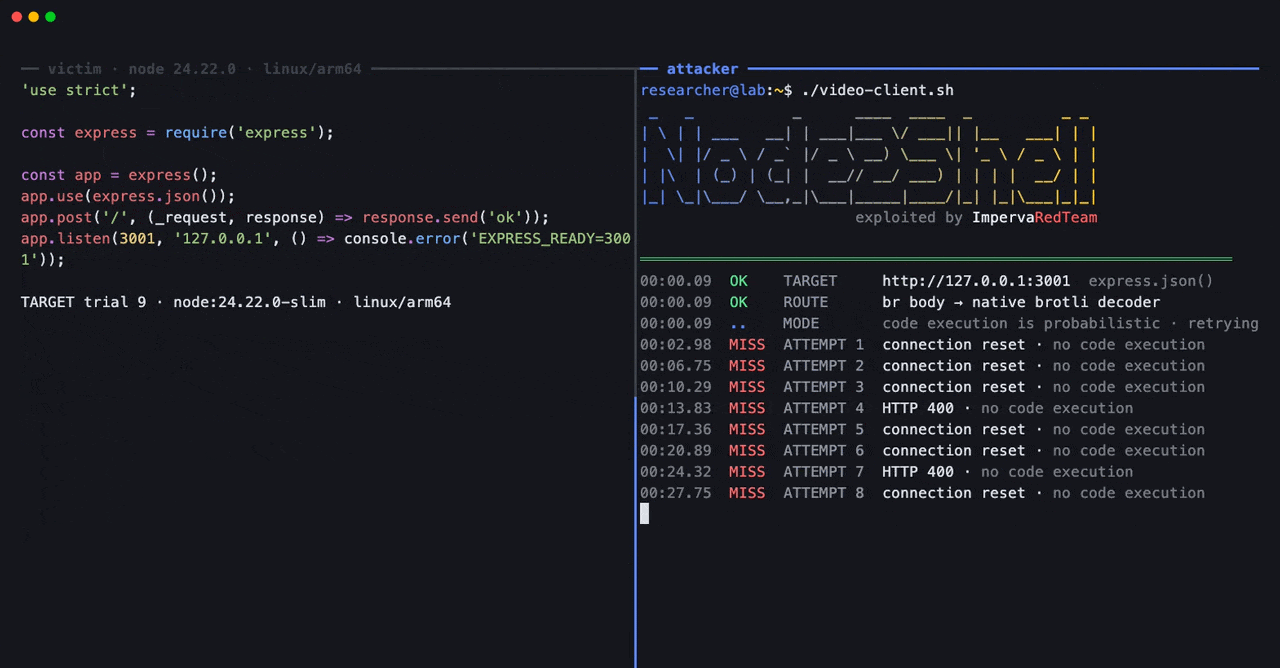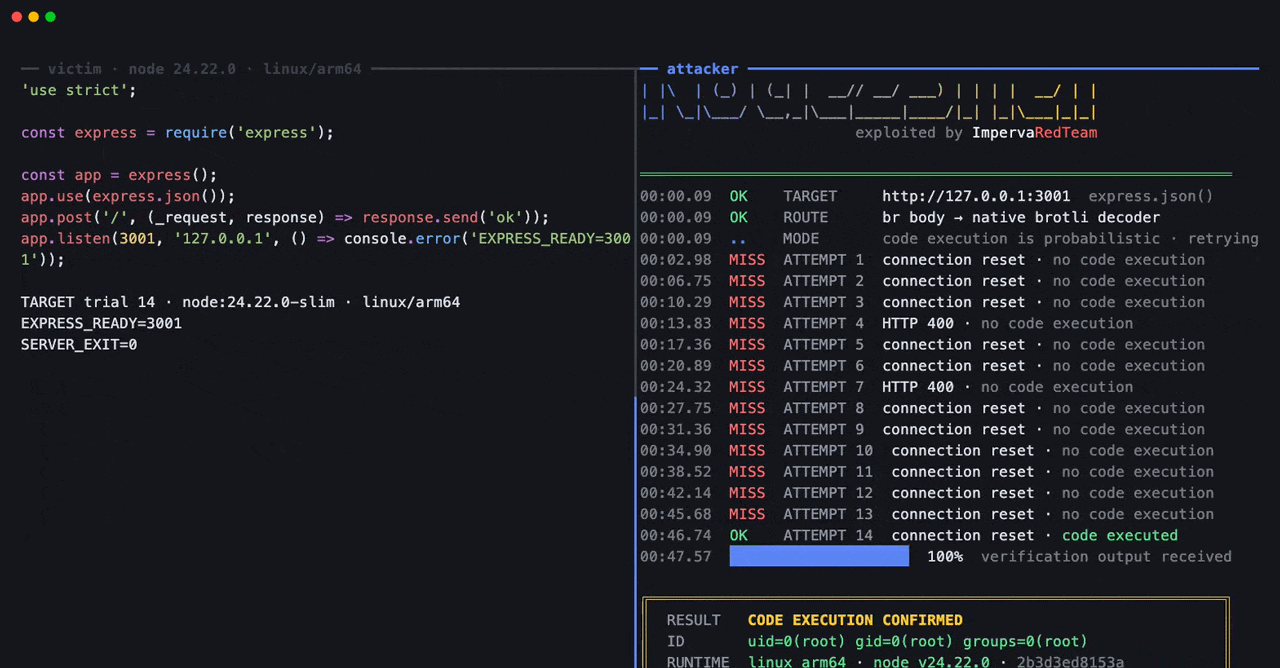
Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their "Node2Shell" proof of concept ran code on the official Node.js 24.22.0 image for Linux arm64, with no debugger or custom build, by feeding crafted data to the bundled Brotli decoder (CVE-2026-111497). Node.js disclosed the flaw
lege.news preia doar titlul și un extras de maximum 500 de caractere. Articolul integral și drepturile asupra conținutului aparțin sursei citate.
Din aceeași categorie · Risc & Fraude