Unpatched Broadcom Wi-Fi Flaw Lets Attackers in Range Run Code as Root on Routers
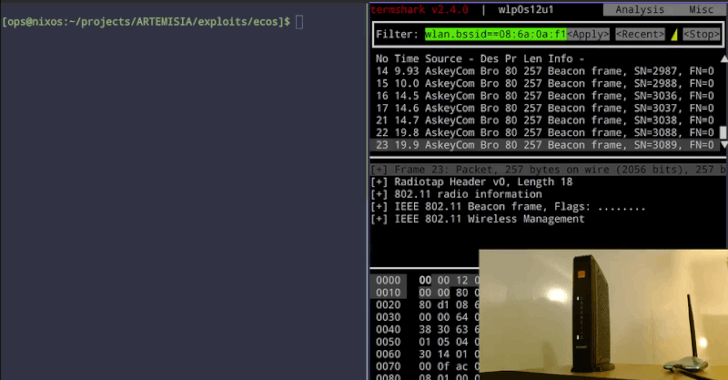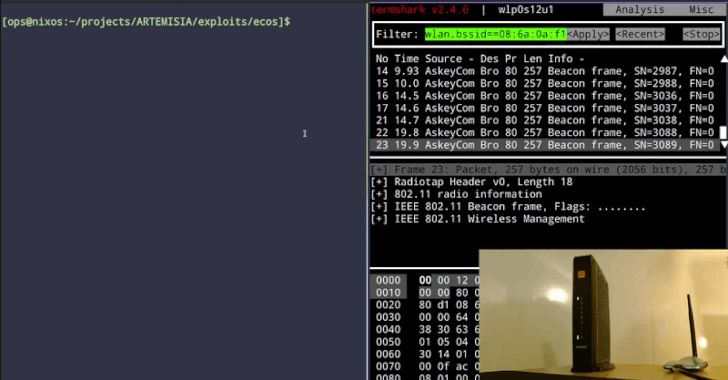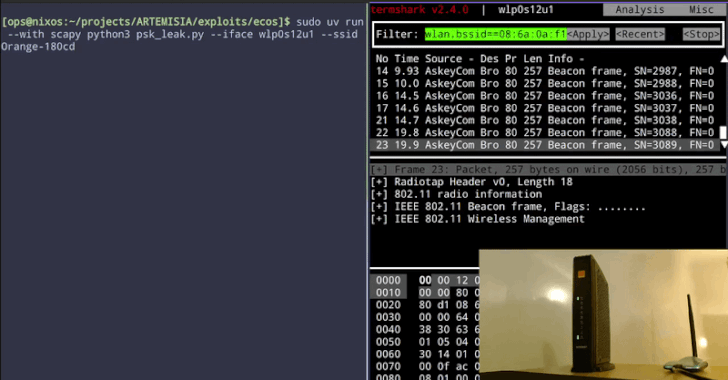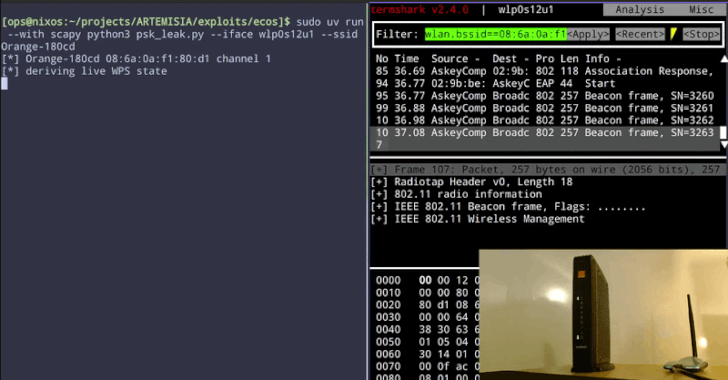
A flaw in Broadcom's Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed on October 16. He showed the attack working against home gateways supplied by three Belgian internet providers, in one case reading the Wi-Fi password off the device
lege.news preia doar titlul și un extras de maximum 500 de caractere. Articolul integral și drepturile asupra conținutului aparțin sursei citate.
Din aceeași categorie · Risc & Fraude